What Is a SOCKS5 Proxy?

Executive Summary
A SOCKS5 proxy is a general-purpose transport-layer proxy protocol defined in RFC 1928 that tunnels arbitrary TCP and UDP traffic between a client and a destination server, without any application-layer inspection or modification. Unlike HTTP and HTTPS proxies — which are Layer 7 tools limited to HTTP/S traffic — SOCKS5 operates at Layer 5 (the Session Layer) and is protocol-agnostic: it can tunnel HTTP, HTTPS, FTP, SMTP, DNS-over-TCP, gaming protocols, torrents, and virtually any other TCP/UDP-based service. This 3,000-word guide covers the complete RFC 1928 handshake, authentication sub-negotiation (RFC 1929), UDP ASSOCIATE for real-time traffic, Python PySocks integration, and a full benchmark comparison against HTTP/HTTPS proxies.
What Is a SOCKS5 Proxy?
SOCKS stands for SOCket Secure — a network protocol designed to relay TCP (and in SOCKS5, UDP) connections through a proxy intermediary. Version 5 of the protocol, standardized in RFC 1928 (1996, updated in 2024 as RFC 9326), introduced three major improvements over SOCKS4: support for UDP proxying (not just TCP), support for IPv6 addressing alongside IPv4 and domain names, and a flexible authentication sub-negotiation system (RFC 1929) that allows the server to choose from multiple authentication methods offered by the client.
From a network architecture perspective, a SOCKS5 proxy sits at the session layer. When a client application (configured to use SOCKS5) connects to a server, the SOCKS5 proxy establishes an actual TCP (or UDP) connection to the target on behalf of the client. The proxy forwards the raw data stream in both directions without reading, modifying, or logging any application-layer content. This is fundamentally different from an HTTPS proxy, which is HTTP-aware and requires the HTTP CONNECT method.
SOCKS5 is the preferred proxy protocol for:
- Non-HTTP traffic: torrenting, gaming, FTP, SMTP, custom TCP services
- Bypass scenarios where HTTP-level inspection or filtering is a concern
- Applications that do not support HTTP CONNECT but do support SOCKS proxy configuration
- Privacy tools like Tor (which uses a SOCKS5 interface by default)
- SSH tunneling configurations (
ssh -Dcreates a local SOCKS5 proxy)
Figure 1 — SOCKS5 vs HTTP/HTTPS Proxy Protocol Stack: Layer, Transport, and Capability Comparison
The SOCKS5 RFC 1928 Handshake: Step by Step
The SOCKS5 connection process is defined precisely in RFC 1928 and consists of three sequential phases: greeting and method negotiation, authentication (if required), and the request/reply exchange. Unlike HTTP proxies, all SOCKS5 communication is binary — not textual HTTP.
Phase 1 — Client Greeting: The client opens a TCP connection to the SOCKS5 server on port 1080 (default) and sends a greeting message: VER=0x05 (SOCKS version 5), NMETHODS=N (number of auth methods the client supports), followed by N method bytes. Common methods are 0x00 (no authentication) and 0x02 (username/password per RFC 1929).
Phase 2 — Server Method Selection: The server selects one of the offered methods and replies with 2 bytes: VER=0x05 and METHOD=chosen_method. If METHOD=0xFF, no acceptable method was found and the connection is rejected. If method 0x02 is chosen, a username/password sub-negotiation round occurs.
Phase 3 — CONNECT/BIND/UDP Request: After authentication, the client sends a request with the desired command: CMD=0x01 (CONNECT — establish a TCP connection), CMD=0x02 (BIND — accept inbound connection), or CMD=0x03 (UDP ASSOCIATE — set up UDP relay). The request includes the target address type (IPv4, domain name, or IPv6) and port. The server opens the connection and replies with the bound address and port on success (REP=0x00).
Figure 2 — RFC 1928 Packet Structure: Client Greeting and CONNECT Request binary format
SOCKS5 Address Types: IPv4, IPv6, and Domain Names
One of SOCKS5's key advantages over SOCKS4 and HTTP proxies is its flexible address type system, defined by the ATYP field in the request packet. SOCKS5 supports three address type values:
ATYP=0x01 — IPv4 address: 4-byte big-endian IPv4 address follows. This is the most common address type for datacenter proxy connections to servers resolved locally.
ATYP=0x03 — Domain name: A length byte is followed by the domain name string. The SOCKS5 server performs DNS resolution on behalf of the client. This is critical for DNS leak prevention — by letting the proxy resolve DNS, the client's DNS queries never leave the local network. This is one of SOCKS5's major privacy advantages over HTTP proxies where the client resolves DNS locally.
ATYP=0x04 — IPv6 address: 16-byte IPv6 address follows. Native SOCKS5 IPv6 support was not available in SOCKS4, making SOCKS5 essential for IPv6-capable proxy infrastructure and modern IPv6 proxy comparisons.
UDP ASSOCIATE: Real-Time Traffic Through SOCKS5
The most significant and unique capability of SOCKS5 — absent from both SOCKS4 and all HTTP/HTTPS proxies — is UDP ASSOCIATE. The CMD=0x03 command instructs the SOCKS5 server to set up a UDP relay session. This is essential for:
- DNS proxying (UDP port 53) — routing DNS queries through the proxy for full anonymization
- Online gaming — game servers predominantly use UDP for low-latency state updates
- VoIP and real-time communication — SIP/RTP protocols use UDP
- Video streaming protocols — QUIC (HTTP/3) and WebRTC use UDP
- BitTorrent — the DHT network and peer-to-peer data transfer use UDP extensively
During UDP ASSOCIATE, the server returns a UDP relay address. The client then sends UDP datagrams to this relay address (wrapped in a SOCKS5 UDP header containing the target address), and the relay forwards them to the actual destination. Responses are wrapped similarly and sent back. Note that most commercial residential proxy services restrict or disable UDP ASSOCIATE due to infrastructure complexity — for full UDP ASSOCIATE support, look for dedicated SOCKS5 proxy providers or datacenter proxies. See our guide on SOCKS5 proxy providers for options with UDP support.
Figure 3 — SOCKS5 CMD Types: CONNECT (TCP outbound), BIND (TCP inbound), UDP ASSOCIATE (UDP relay)
SOCKS5 Authentication: Username/Password (RFC 1929)
When the server selects method 0x02 (username/password authentication), the RFC 1929 sub-negotiation proceeds. The client sends: VER=0x01 (sub-negotiation version), ULEN=N, UNAME (N bytes), PLEN=M, PASSWD (M bytes). The server responds with VER=0x01 and STATUS: 0x00 means success, any other byte means failure (and the connection is closed).
All commercial proxy authentication for SOCKS5 services uses this username/password method. The credentials are sent in plaintext (not encrypted) within the SOCKS5 handshake itself. This means the connection between client and proxy must be trusted — on untrusted networks, consider wrapping the SOCKS5 connection inside an SSH tunnel or TLS layer. For GSSAPI authentication (METHOD=0x01), which provides Kerberos-based authentication, see RFC 1961 — it is used in enterprise environments but rarely in commercial proxy services.
Python SOCKS5 Integration with PySocks and httpx
Python supports SOCKS5 proxying via the PySocks library (which monkey-patches the socket module) and natively in httpx and aiohttp via the socks connector. Below are production-ready configuration patterns:
Figure 4 — Python SOCKS5 proxy configuration: requests with socks5h:// and async httpx
The critical distinction between socks5:// and socks5h:// (SOCKS5 with hostname resolution): socks5h:// sends the domain name to the proxy for resolution (using ATYP=0x03), preventing DNS leaks. Always use socks5h:// when privacy or bypassing DNS-based geo-restrictions is a goal.
SOCKS5 Performance Benchmarks
SOCKS5 proxies introduce minimal overhead compared to HTTP/HTTPS proxies for HTTPS traffic because the handshake is simpler (binary, fewer round trips) and there is no HTTP header parsing at the proxy layer. However, for pure HTTP/S scraping workflows, the performance difference between SOCKS5 and HTTP CONNECT is negligible in practice — both require one TCP round trip to establish the tunnel.
| Metric | SOCKS5 | HTTP CONNECT | SOCKS4 | Notes |
|---|---|---|---|---|
| Handshake RTTs | 1–2 RTTs | 1–2 RTTs | 1 RTT | +1 RTT if auth |
| TCP Support | ✓ Full | ✓ Full | ✓ Full | |
| UDP Support | ✓ Via ASSOCIATE | ✗ No | ✗ No | Key differentiator |
| IPv6 Support | ✓ Native | Partial | ✗ No | ATYP=0x04 |
| DNS Leak Prevention | ✓ socks5h:// | ✗ Client resolves | ✗ No | Privacy critical |
| Authentication | User/pass + GSSAPI | Basic + Digest | User ID only | RFC 1929 |
SOCKS5 in Real-World Proxy Infrastructure
Most commercial proxy providers — including Bright Data, Oxylabs, and Decodo — support SOCKS5 protocol access to their residential and datacenter proxy pools, typically alongside HTTP/HTTPS. The choice between SOCKS5 and HTTP/HTTPS at the application configuration level does not affect which IPs you get — it only changes how your client negotiates the tunnel.
For web scraping specifically, HTTP/HTTPS proxies have a slight advantage in tooling compatibility because more libraries default to HTTP proxy configuration. But for Playwright/Puppeteer, SOCKS5 configuration is equally well-supported. Rotating proxy pools work identically over SOCKS5 — the rotation happens at the proxy server regardless of the protocol used by the client to connect.
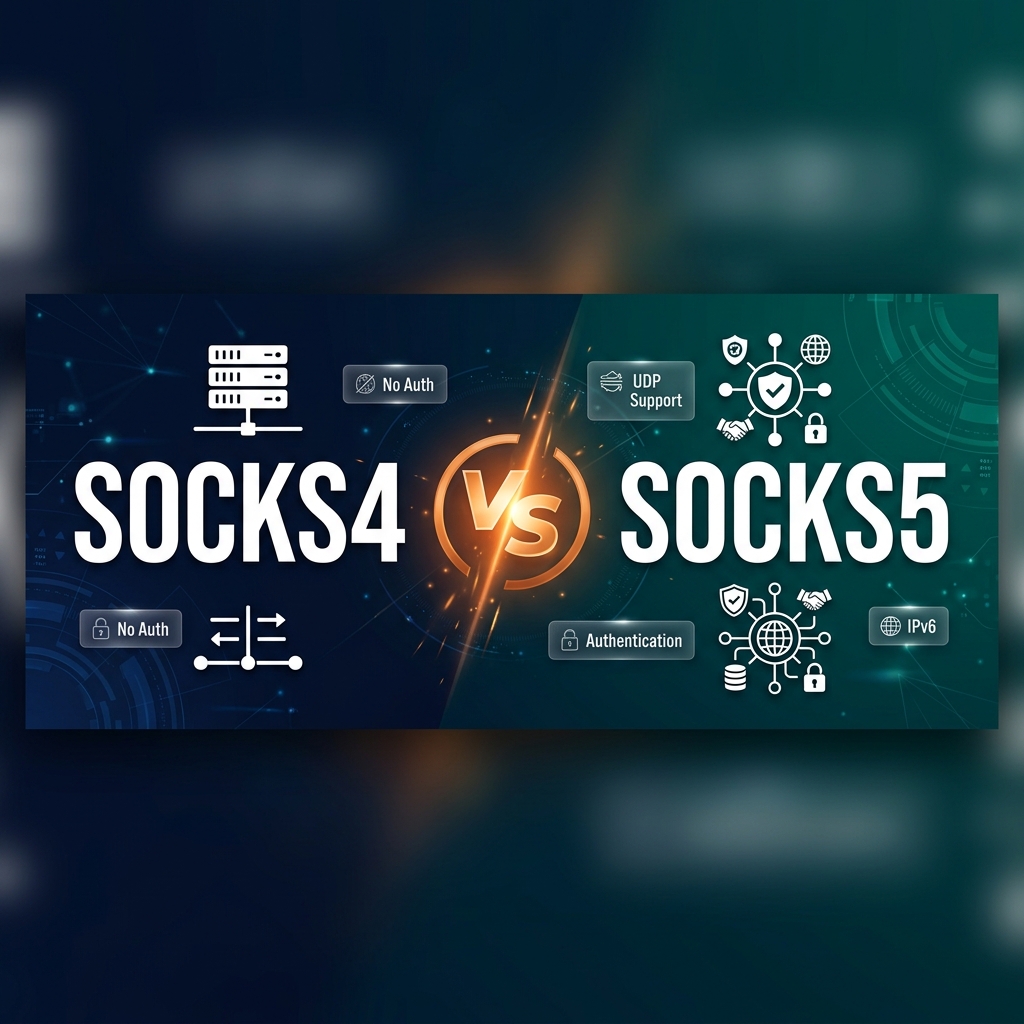
For non-HTTP use cases — especially social media automation tools that use custom TCP sockets, gaming infrastructure, or any UDP-dependent service — SOCKS5 is the only viable proxy protocol. Our SOCKS4 vs SOCKS5 comparison provides a detailed analysis of when to choose each version.
Frequently Asked Questions About SOCKS5 Proxies
What port does SOCKS5 use?
The default IANA-registered port for SOCKS5 is 1080. Many commercial proxy providers also offer SOCKS5 on alternative ports (e.g., 10080, 5000) to bypass firewall restrictions. You configure the SOCKS5 proxy host and port in your application the same way as an HTTP proxy host and port — they are independent of the destination server port.
Does SOCKS5 encrypt my traffic?
No. SOCKS5 itself does not provide encryption — it is a tunneling protocol, not an encryption protocol. The SOCKS5 handshake (including authentication) is sent in plaintext. If you connect to an HTTPS site via SOCKS5, the TLS encryption is between your browser/app and the destination server — the SOCKS5 layer carries the encrypted bytes. For full encryption including the proxy connection itself, use SSH dynamic forwarding (ssh -D 1080) which wraps SOCKS5 inside an SSH tunnel, or a VPN.
Is SOCKS5 better than HTTP proxy for web scraping?
For pure HTTPS web scraping, performance is comparable. HTTP CONNECT proxies may be marginally simpler to configure in some libraries. SOCKS5 provides better DNS leak prevention (via socks5h://) and is necessary if your scraping infrastructure also handles non-HTTP protocols. For dedicated HTTP/HTTPS scraping, either protocol works well — choose based on what your proxy provider supports and what your client library handles most naturally.
Can I use SOCKS5 with a browser?
Yes. All major browsers (Chrome, Firefox, Safari, Edge) support SOCKS5 proxy configuration natively. In Firefox, it's under Network Settings → Manual proxy configuration → SOCKS Host. Chrome uses system-level proxy settings. Playwright and Puppeteer browser automation frameworks also support SOCKS5 via the --proxy-server launch flag using the socks5:// scheme.
Internal Resources on Proxy Protocols
- SOCKS4 vs SOCKS5: Which Is Better?
- What Is an HTTPS Proxy? — TLS Tunnel Architecture
- What Is an HTTP Proxy? — Architecture, Protocols & Security
- SOCKS5 vs HTTP Proxies: Technical Differences That Matter
- Proxy Authentication Methods Explained
- What Is a Rotating Proxy?
- Best Proxies for Web Scraping 2026
- Types of Proxy Servers Explained: Complete Technical Guide
- Residential Proxies in 2026: Complete Guide
- Best IPv4 vs IPv6 Proxies: Benchmark Results
Written by PROXYIP
Our editorial team consists of network engineers and data scraping experts dedicated to bringing transparency to the proxy market. We specialize in distributed infrastructure and high-scale data acquisition.